Guides
Sacramento and the California Age-Appropriate Design Code, a guide for social apps
California's Age-Appropriate Design Code makes child privacy a product decision for social apps, with duties set in Sacramento and enforced by the attorney general.
What to take away
- The California Age-Appropriate Design Code is a state statute, drafted and passed in Sacramento, that makes child privacy a product decision rather than a settings menu.
- It defines a child as anyone under 18, which is wider than the federal under-13 line, so more of a social app's user base falls inside it.
- The duties are defaults, data minimisation, and a documented impact assessment, plus age assurance where a service needs an age signal.
- The California Attorney General enforces it, with civil penalties calculated per affected child, and federal COPPA still applies on top.
- No part of this is legal advice; coverage questions belong with qualified California counsel.
How Sacramento writes the rules social apps must follow
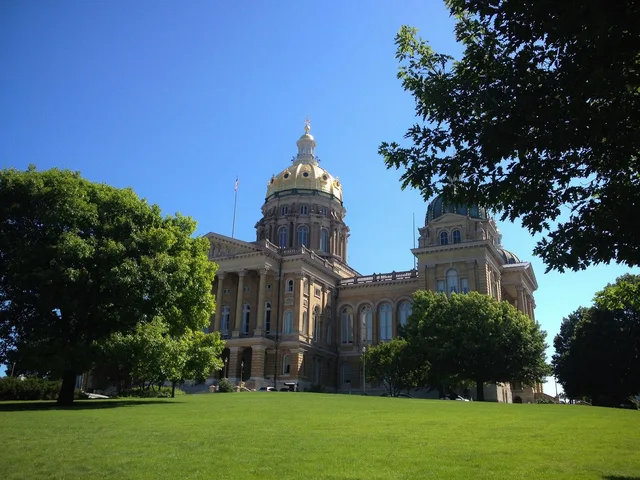
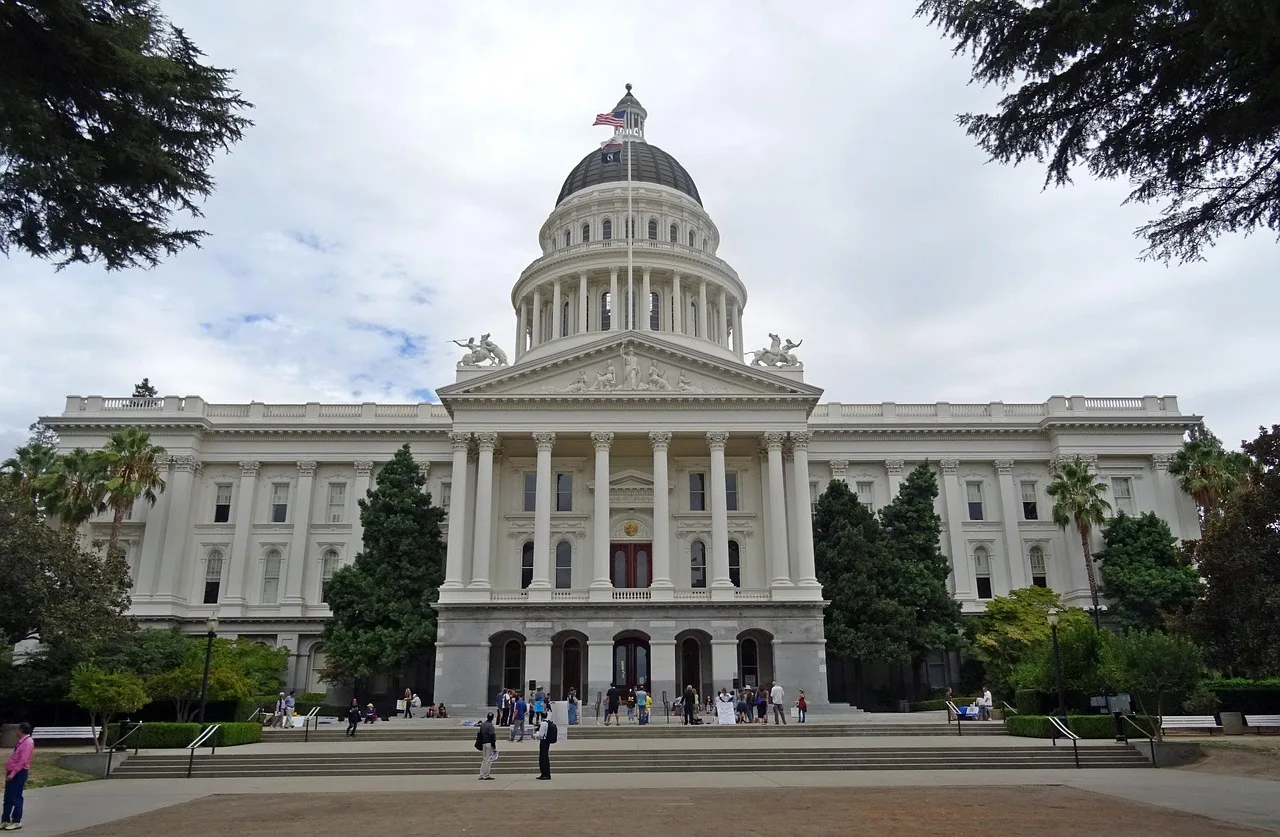
Sacramento is where the California legislature sits, and the Age-Appropriate Design Code was negotiated, amended and voted on in the Capitol on 10th Street. The statute is the California Age-Appropriate Design Code Act, Assembly Bill 2273, signed on September 15, 2022 and codified at California Civil Code sections 1798.99.28 to 1798.99.35.
It was set to take effect on July 1, 2024. In September 2024, the federal district court in NetChoice v. Bonta issued a preliminary injunction blocking enforcement of the Act in its entirety while the appeal proceeds. The injunction means the state cannot currently enforce the Act; it does not repeal the statute or resolve the case on the merits. California's appeal was pending when this was written.
California moves first on tech regulation more often than most states. A social app operating anywhere in the United States almost always has California users. So a rule passed in Sacramento lands on product roadmaps in Menlo Park, Seattle, New York and Austin. This happens whether or not those teams planned for it.
State law does not replace federal law here. The Federal Trade Commission enforces the Children's Online Privacy Protection Rule, which implements the Children's Online Privacy Protection Act (COPPA). COPPA generally applies to child-directed online services and to general-audience services with actual knowledge they collect personal information from children under 13; covered operators must provide notice and obtain verifiable parental consent. It operates alongside the California code.
What the code actually requires
The code requires covered businesses to treat the best interests of children as a design input when they build services likely to be accessed by children. Covered services include social apps, games, and most online products a child is likely to open.
The definition of a child is anyone under 18. That single line pulls teenagers into a rule that federal law leaves mostly alone, and it changes how much of a user base needs child-facing treatment.
The code sets duties, not one ban. A business must assess whether its design could harm children and must keep that assessment on file. It must also configure privacy settings for children differently from adults, so protections sit in the default state of the product rather than behind a menu a child has to find.
The data protection impact assessment must be completed before a covered service, product, or feature is offered—not merely before it collects a child's data. It should document the feature's purpose, how it uses children's personal information, risks of material detriment to children, and safeguards planned to address those risks, and assess whether the design is consistent with children's best interests.
The Quebec privacy law puts duties on platforms that serve younger users, but Quebec's regulator does not enforce the way the California attorney general does.
Design duties: defaults, data minimisation and age assurance
Three categories cover most of the operational work: default settings, data minimisation, and age assurance or age estimation.
Defaults must sit at the highest privacy level unless the business can justify a different choice for a child. No public-by-default profiles for minors, no location sharing switched on at signup, no contact discovery running before the user deliberately turns it on.
Data minimisation means collecting only what the feature in front of the user actually needs. If a social app does not need a precise birth date for a core function, it should not demand one. If it needs an age signal, it should take the least identifying version that works.
Age assurance is the hardest piece, and the code mandates no single technology. Operators can use estimation, verification, or another method reasonably designed to work out whether a user is a child. The method must not collect more data than that purpose requires.
Named methods include facial age estimation from Yoti and VerifyMy, document checks from Jumio, Persona and Incode, and platform signals such as Apple's Declared Age Range API and Google Play's age signals API.
A practical sequence for a compliance team is to:
- Determine whether the service is likely to be accessed by children in California and document the basis for that decision.
- Inventory the service's features and map what personal information each collects, uses, or shares.
- Complete the data protection impact assessment before offering covered features, documenting their purpose, risks to children, and planned safeguards.
- Review privacy defaults and data collection, including public profiles, location sharing, and contact discovery.
- Choose whether to estimate users' ages or apply child privacy protections to everyone, and select a method proportionate to the risks.
- Assign an owner for the assessment and keep a change log and records of design decisions.
Compliance Sequence for Social Apps
- Map fields collected from users under 18
- Set child-facing defaults to most private
- Choose proportionate age-assurance method
- Run and maintain impact assessment
- Re-test defaults after onboarding changes
Pew Research Center tracks how age groups use social platforms, and its age and generations research helps size the under-18 population inside an app. Those usage patterns shape which features count as likely to be accessed by children.
Who enforces the code, and what a penalty looks like
California Attorney General Rob Bonta is the primary enforcer. The Act authorizes the attorney general to bring civil actions against covered businesses that breach its design duties; no separate state agency was created for this code. Because enforcement is enjoined, the attorney general cannot currently enforce the Act, and no enforcement action has been brought under it.
Penalty exposure is calculated per affected child. The statutory maximum is $2,500 per affected child for each negligent violation and $7,500 per affected child for each intentional violation.
The law also allows injunctive relief, meaning a court can order changes to the product itself.
Enforcement usually opens with an investigation and a request for records, including the impact assessments. A company that cannot produce a current assessment is in a weak position even when the product is otherwise sound.
The FTC stays active in the same territory. Its COPPA compliance guidance explains the federal obligations for apps that collect data from children under 13.
Section 230 of the Communications Decency Act does not shield a platform from design and privacy claims. It limits liability for third-party content, not for a company's own product decisions, and that distinction is routinely misread in policy arguments.
What a social app should change first
Start with the items carrying the most legal risk and the least engineering effort. Defaults and documentation are natural early priorities. Age assurance can take longer because it touches onboarding, identity, and vendor selection.
Use this first-90-days checklist as an internal work plan, not as a statutory deadline:
- Confirm whether the app is likely to be accessed by children in California and record the coverage rationale.
- Map the app's features, data flows, and privacy settings; identify public profiles, location sharing, and contact discovery that are on by default.
- Complete or update the impact assessment for covered features before offering them, and document risks and safeguards.
- Change defaults and reduce collection to what each feature needs.
- Evaluate age estimation, verification, or protections for all users; document why the chosen approach fits the risks and minimizes data collection.
- Assign owners for follow-up, retain design decisions and change records, and prepare to respond to an attorney general records request.
- Review COPPA obligations for users under 13 alongside the California requirements.
First 90 Days Checklist
- Decide if app likely accessed by children
- Inventory signup and first-session fields
- Set child-facing defaults to most private
- Select age-assurance method, record minimum data
- Complete and store impact assessment
- Add release review for default changes
- Train support on child-privacy escalations
Designers should treat the impact assessment as a design document rather than a legal appendix. A feature that cannot be explained in the assessment without collecting extra data is a feature that needs redesigning.
Public debate about social media and harms to younger users can shape how regulators read the design duties. A compliance lead should be able to explain how the product's design choices address those concerns.
Keep a change log. When the attorney general asks how a default was set six months ago, a dated record is the difference between a clean answer and an expensive one.
Common questions
Does the code apply to an app with no California users?
It reaches businesses that provide services likely to be accessed by children in California. If a social app has California users under 18, assume coverage and take advice from California counsel before deciding otherwise.
What is the difference between age assurance and age verification?
Age assurance is the broad category, covering any method that estimates or confirms a user's age. Age verification is the narrower approach that confirms age, often with stronger identity signals. The code permits either where the method is proportionate.
Can a social app simply ask for a birth date?
It can, but data minimisation duties mean it should not collect more than the feature needs. A full birth date is often more identifying than the function requires, so many teams use age bands or estimation instead.
Do federal COPPA rules still apply?
Yes. COPPA covers children under 13 and continues to run alongside state law. The FTC publishes compliance guidance for operators that sets out the federal requirements.